

A certificate manager keeps track of the digital certificates that secure your websites and internal services. Selecting the right one for your organization depends on the environment you need to cover.
Public Transport Layer Security (TLS) certificates will be limited to 47 days by March 2029, which means renewing all of your certificates several times a year.
This guide compares seven certificate managers across enterprise, Kubernetes, and web server environments, along with the pros and cons of each. The AppViewX team researched it using adoption data, practitioner discussions on Reddit and review sites, analyst reports, and each tool’s documented features. AppViewX is one of the tools ranked.
Key takeaways
- Choosing a certificate manager starts with knowing how many certificates you have and where they run. Large companies with many teams need an enterprise platform, and teams with a few websites can start with a free tool.
- AppViewX is the top pick for enterprises. It tracks certificates automatically, renews each one before expiry, and holds a Leader placement from research firm IDC.
- For Kubernetes, the usual choice is cert-manager, a free open-source CNCF project. AppViewX CLM can manage its certificates alongside your others.
- Free tools save on licensing but need engineers to run them. Many companies add a commercial certificate manager as they grow.
What a certificate manager does
Every HTTPS connection and service-to-service request relies on a certificate that proves the endpoint is who it claims to be. Keeping those certificates current is what keeps services trusted.
A certificate manager takes that lifecycle off your team’s plate. It requests certificates from a certificate authority (CA), installs them, tracks their expiry dates, and renews them automatically. Enterprise tools add discovery and policy controls on top. If you’re new to this, start with how certificate automation works.
Kubernetes adds to that volume. 82% of container users now run it in production.
How we picked these certificate managers
Many certificate tools have few formal reviews, so we compared them on four signals:
- Adoption: download and market share data, especially for open-source projects
- Practitioner feedback: what sysadmins and platform engineers say on Reddit and in peer-review communities
- Analyst recognition: placements in independent analyst research
- Documented capabilities: discovery and automation depth
We ranked the tools by how much of an organization’s certificate estate each one can cover, from full enterprise coverage down to single-environment tools.
Table 1. Top certificate managers by use case
| Rank | Tool | Use case | Type |
| 1 | AppViewX | Enterprise CLM | Commercial |
| 2 | Keyfactor Command | Enterprise CLM | Commercial |
| 3 | DigiCert Trust Lifecycle Manager | Enterprise CLM | Commercial |
| 4 | cert-manager | Kubernetes | Open source |
| 5 | IBM Vault | Kubernetes and secrets | Open source and commercial |
| 6 | Certbot | SSL and web servers | Open source |
| 7 | AWS Certificate Manager | SSL on AWS | Cloud service |
Source: AppViewX analysis of the sources cited below.
Best certificate managers for enterprise CLM
Enterprise certificate lifecycle management (CLM) platforms manage certificates across the environments and CAs a company uses. They suit organizations with thousands of certificates and audit requirements to meet.
#1 AppViewX
Best for: enterprises with certificates spread across many teams and CAs
AppViewX automates certificate management across the enterprise. Smart Discovery scans cloud and on-premises environments for certificates, including unmanaged ones, and brings them into a single inventory with assigned owners.
Closed-loop automation covers renewal end-to-end, from issuing new certificates to pushing them to the endpoints that use them. AppViewX also automates renewal cycles and re-enrollment policies to keep pace with each step of the CA/Browser Forum schedule.
AppViewX was named a Leader in the 2026 IDC MarketScape for worldwide CLM software, and PeerSpot reviewers report that its automation has reduced human errors.
In a Forrester TEI study commissioned by AppViewX, a composite customer organization saw a 302% return on investment over three years. Forrester also found that manual renewals took about 30 minutes per certificate, compared with about 15 seconds through AppViewX.
Pros
- Agentless discovery finds certificates across hybrid and multi-cloud environments
- Automated installation on F5 load balancers and web servers
- Post-quantum readiness with bulk certificate reissuance
- An audit trail for every certificate action
- A self-service portal for public key infrastructure (PKI) teams
Cons
- Pricing comes through a custom quote, with no list price to compare against.
- Some reviewers find the interface complex at times.
To see how AppViewX would handle your own certificates, speak with an AppViewX expert today.
#2 Keyfactor Command
Best for: organizations that already run Microsoft’s own certificate services
Keyfactor Command is a CLM platform that manages certificates across public CAs, Microsoft Active Directory Certificate Services (AD CS), and its own EJBCA private CA, with typical entry deals of around $75,000 a year.
Pros
- Suits teams running Microsoft AD CS, since it manages those certificates alongside ones from public CAs
- Lets you run the CA and the lifecycle manager from one vendor and cuts down on integrations to maintain
Cons
- Quote-based pricing with no public price list makes early budgeting harder.
- The installation process can be complex, so plan extra time and in-house expertise for the rollout.
#3 DigiCert Trust Lifecycle Manager
Best for: companies that source most of their certificates from DigiCert
DigiCert Trust Lifecycle Manager pairs certificate management with DigiCert’s own public CA, and independent reviewers note that it combines public trust with lifecycle software. It runs as a SaaS product on the DigiCert ONE platform. Its G2 reviewer base leans toward the middle of the market, with 45.5% of reviews coming from mid-sized companies.
Pros
- Combines issuance and lifecycle management under one vendor for simpler contracts and support
- Brings post-quantum work to prepare for newer algorithms
Cons
- Works best with DigiCert as the issuing CA. Moving certificates elsewhere gets harder if your CA strategy changes.
- Costs add up across a custom subscription plus separate per-certificate fees through CertCentral, and the total is harder to predict.
Best certificate managers for Kubernetes
Kubernetes creates and retires workloads often, and each one may need its own certificate. Tools in this group run inside the cluster and issue certificates automatically as services start.
#4 cert-manager
Best for: platform teams that want certificates managed natively inside Kubernetes
Most Kubernetes teams manage certificates with cert-manager, an open-source project hosted by the Cloud Native Computing Foundation (CNCF). At its CNCF graduation in November 2024, the project counted 500 million downloads a month and more than 450 contributors, and user research suggested 86% of new production clusters were created with it deployed as standard practice. Sysadmins discussing renewal tooling on Reddit call it the answer for Kubernetes.
AppViewX CLM can discover Kubernetes certificates issued by cert-manager and track them alongside the rest of your inventory.
Pros
- Free and open source, with an active contributor community
- Issues and renews certificates inside Kubernetes and attaches them to services automatically
Cons
- Has no view of unmanaged certificates outside its control, so manually created ones need separate tracking
- Expiry alerts depend on separate tools such as Prometheus, another system to set up and watch.
#5 IBM Vault
Best for: DevOps teams that already use Vault for secrets
IBM Vault (formerly HashiCorp Vault) is a secrets manager that can also act as a private CA, issuing short-lived certificates for internal services.
Pros
- Keeps secrets secure and easy to manage in one place
- Lets teams that already use Vault for passwords and keys issue certificates from the same system
Cons
- Has a steep learning curve, so teams new to Vault should plan for time to get comfortable with it.
- Issues private certificates only, so public-facing sites still need a separate CA.
Best certificate managers for SSL and web servers
Smaller environments with a few public websites mainly need a reliable way to get SSL/TLS certificates and renew them on schedule. These tools cover that with little or no cost, and a free SSL/TLS certificate scan shows what you’re already running.
#6 Certbot
Best for: teams that want an automated client for public-facing sites
Certbot is an open-source tool from the Electronic Frontier Foundation, most often used with Let’s Encrypt. That CA grew from serving 492 million websites to 762 million in 2025, and it plans to cut its default certificate lifetime to 45 days by 2028, ahead of the industry-wide 47-day limit in 2029. That plan is the latest of several Let’s Encrypt renewal changes.
Certificates that Certbot issues on public sites also show up in AppViewX discovery scans and can sit in the same inventory as the rest of your estate.
Pros
- Issues certificates at no cost from the largest CA by volume
- Can run scripts automatically after each renewal, such as restarting a web server
Cons
- Frequent renewals can break internal apps that expect a fixed configuration.
- Built-in installers cover Apache and Nginx, while other server software depends on third-party plugins or custom deploy hooks.
#7 AWS Certificate Manager
Best for: teams whose infrastructure sits fully on AWS
AWS Certificate Manager (ACM) issues and renews certificates for AWS resources such as load balancers and CloudFront. It holds an 11% mindshare in PeerSpot’s certificate management category, and PeerSpot reviewers say it gives them central lifecycle control that helps improve security. It also has limits outside AWS that matter for hybrid estates.
Teams that run ACM alongside other tools can manage ACM certificates from the same AppViewX inventory.
Pros
- Automatic provisioning and renewal for integrated services, with no manual steps once certificates are attached.
- Certificates attached to integrated services come at no charge.
Cons
- Exportable certificates cost extra for use outside AWS, and the fees add up across many domains.
- Tracks only certificates on AWS resources, so certificates on-premises or in other clouds need a separate tool.
Open-source vs commercial certificate managers
Table 2 compares open-source and commercial certificate managers on cost, scope, discovery, support, and governance.
Table 2. Open-source and commercial certificate managers compared
| Factor | Open source (cert-manager, Certbot) | Commercial CLM (AppViewX, Keyfactor, DigiCert) |
| License cost | Free | Custom quote |
| Scope | One cluster or server | Whole enterprise |
| Discovery | None | Continuous across environments |
| Support | Community forums | Vendor support teams |
| Governance and audit | Built by your team | Included |
Source: AppViewX analysis.
Open-source tools often come first, and a commercial platform joins them as needs grow.
How to choose a certificate manager
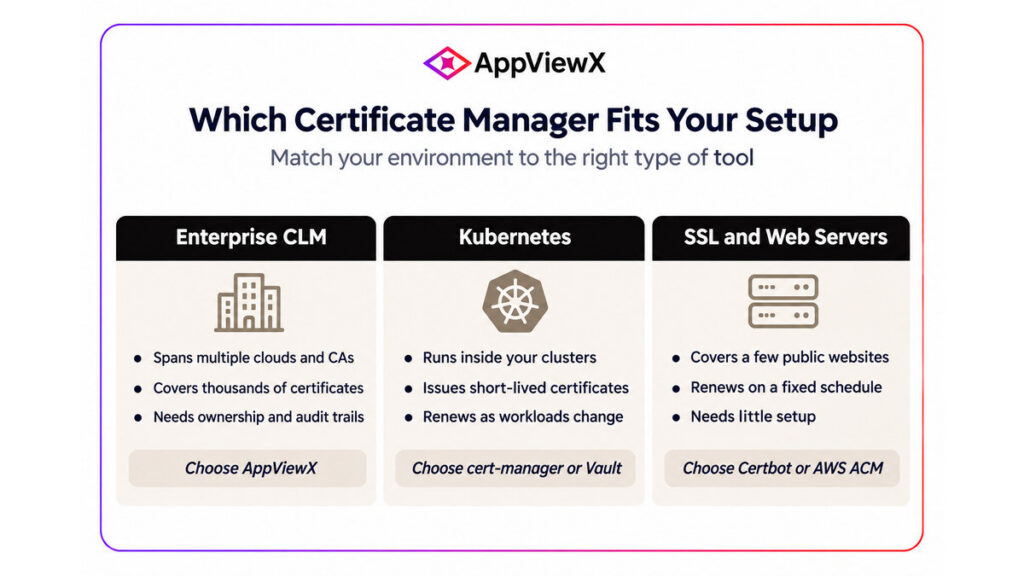
Figure 1. Matching a certificate manager to your environment
Use these questions to match a tool to your setup, and check the must-have CLM requirements before shortlisting vendors.
- How many certificates do you manage? A few dozen on web servers suit Certbot. Thousands across teams call for an enterprise CLM platform.
- Where do they live? Kubernetes-heavy teams need cert-manager or Vault, and AWS-hosted applications fit AWS Certificate Manager.
- How many CAs do you use? Multiple public and private CAs point to a CA-agnostic platform such as AppViewX. Ask vendors to verify CA-agnostic claims in a demo.
Why enterprises choose AppViewX for certificate management
AppViewX pulls certificates from cert-manager, Certbot, cloud services, and internal CAs into a central view, and applies the same policy to all of them without replacing the tools that issue them.
Disclaimer: Facts checked 12th November 2026. Product features and adoption figures change often and should be confirmed with each vendor.
Frequently asked questions
Does the 47-day limit apply to private certificates?
No. The CA/Browser Forum schedule covers publicly trusted TLS certificates, and internal certificates aren’t subject to its rules. A private CA, such as IBM Vault, sets its own validity periods for the certificates it issues.
Does Certbot work with CAs other than Let’s Encrypt?
Yes. Certbot can act as a client for any CA that supports the ACME protocol, which includes several commercial CAs and private CAs set up for internal use.
What is the ACME protocol?
ACME (Automatic Certificate Management Environment) is an open standard that lets software request and renew certificates from a CA without manual steps. Certbot, cert-manager, and most enterprise CLM platforms use it to automate renewal.
Sources
- CA/Browser Forum, Ballot SC-081v3 (April 11, 2025): https://cabforum.org/2025/04/11/ballot-sc081v3-introduce-schedule-of-reducing-validity-and-data-reuse-periods/
- AppViewX, 47-day mandate compliance guide: https://www.appviewx.com/blogs/47-day-mandate-compliance-guide/
- AppViewX, Certificate automation: how it works and what to look for: https://www.appviewx.com/blogs/certificate-automation-how-it-works-and-what-to-look-for/
- CNCF, Annual Cloud Native Survey report: https://www.cncf.io/reports/the-cncf-annual-cloud-native-survey/
- AppViewX, Best certificate lifecycle management software 2026: https://www.appviewx.com/blogs/best-certificate-lifecycle-management-software-2026/
- AppViewX, Certificate lifecycle management software: https://www.appviewx.com/products/certificate-lifecycle-management-software/
- AppViewX, Smart Discovery: https://www.appviewx.com/solutions/clm-smart-discovery/
- AppViewX, Closed-loop automation: https://www.appviewx.com/solutions/clm-closed-loop-automation/
- AppViewX, November 2025 product release: https://www.appviewx.com/blogs/november-2025-product-release/
- AppViewX, IDC MarketScape for CLM: https://www.appviewx.com/idc-marketscape-on-certificate-lifecycle-management/
- PeerSpot, AppViewX vs. DigiCert PKI Platform: https://www.peerspot.com/products/comparisons/appviewx-cert_vs_digicert-pki-platform
- Forrester, The Total Economic Impact of the AppViewX Platform (commissioned by AppViewX, February 2026): https://tei.forrester.com/go/appviewx/certificatelifecyclemanagement
- AppViewX, Total Economic Impact study news release (March 12, 2026): https://www.appviewx.com/news/with-march-15-ca-browser-forum-deadline-looming-total-economic-impact-study-quantifies-benefits-of-automating-certificate-lifecycle-management/
- AppViewX, Agent vs agentless deployment for CLM: https://www.appviewx.com/blogs/agent-vs-agentless-which-deployment-to-choose-for-certificate-lifecycle-management/
- AppViewX, Simplifying automation of certificate binding to load balancing applications: https://www.appviewx.com/blogs/simplifying-automation-of-certificate-binding-to-load-balancing-applications/
- AppViewX, Crypto-agility and post-quantum cryptography readiness: https://www.appviewx.com/solutions/crypto-agility-and-post-quantum-cryptography-readiness/
- AppViewX documentation, Certificate lifecycle management: https://docs.appviewx.com/2026.2.0/oxy_ex/certificate_lifecycle_managemnt_chapter.html
- AppViewX, Certificate lifecycle management: https://www.appviewx.com/solutions/certificate-lifecycle-management/
- G2, AppViewX vs. Keyfactor Command: https://www.g2.com/compare/appviewx-cert-vs-keyfactor-command
- G2, AppViewX reviews: https://www.g2.com/products/appviewx-cert/reviews
- CiphersSecurity, Best PKI certificate management tools in 2026: https://cipherssecurity.com/best-pki-certificate-management-tools-2026/
- G2, Keyfactor Command review 11530078: https://www.g2.com/products/keyfactor-command/reviews/keyfactor-command-review-11530078
- YesPress, Keyfactor company profile: https://yespress.io/keyfactor
- Deepak Gupta, Top 5 PKI and certificate lifecycle management tools: https://guptadeepak.com/tools/top-5-pki-certificate-lifecycle-management-tools-2026/
- G2, AppViewX vs. DigiCert Trust Lifecycle Manager: https://www.g2.com/compare/appviewx-cert-vs-digicert-digicert-trust-lifecycle-manager
- CNCF, cert-manager graduation announcement (November 12, 2024): https://www.cncf.io/announcements/2024/11/12/cloud-native-computing-foundation-announces-cert-manager-graduation/
- Reddit, Renewal tooling thread: https://www.reddit.com/comments/1tgqbwg/
- AppViewX, Securing modern applications in Amazon EKS with AVX ONE CLM for Kubernetes: https://www.appviewx.com/blogs/securing-modern-applications-in-amazon-eks-with-avx-one-clm-for-kubernetes/
- Reddit, Monitoring certificates outside cert-manager: https://www.reddit.com/comments/1q0nvh2/
- G2, IBM Vault (formerly HashiCorp Vault) review 8720580: https://g2.com/products/hashicorp-vault/reviews/hashicorp-vault-review-8720580
- AppViewX, How to automate SSL certificate renewal: https://www.appviewx.com/blogs/how-to-automate-ssl-certificate-renewal/
- AppViewX, Free SSL/TLS certificate scan: https://www.appviewx.com/free-ssl-tls-certificate-scan/
- EFF, Certbot: https://certbot.eff.org/
- Let’s Encrypt, 2025 end-of-year letter (December 29, 2025): https://letsencrypt.org/2025/12/29/eoy-letter-2025.html
- Let’s Encrypt, From 90 to 45 days (December 2, 2025): https://letsencrypt.org/2025/12/02/from-90-to-45.html
- AppViewX, Let’s Encrypt May 13 changes and renewal updates: https://www.appviewx.com/blogs/lets-encrypt-may-13-changes-renewal-updates/
- Let’s Encrypt, 10 years of Let’s Encrypt (December 9, 2025): https://letsencrypt.org/2025/12/09/10-years.html
- Reddit, Certbot renewals breaking internal apps: https://www.reddit.com/comments/1szrt7c/
- PeerSpot, AWS Certificate Manager vs. EJBCA Enterprise: https://www.peerspot.com/products/comparisons/aws-certificate-manager_vs_ejbca-enterprise
- PeerSpot, AppViewX vs. AWS Certificate Manager: https://www.peerspot.com/products/comparisons/appviewx-cert_vs_aws-certificate-management
- AppViewX, AWS Certificate Manager limitations: https://www.appviewx.com/blogs/aws-certificate-manager-limitations/
- AppViewX, CLM automation with AWS Certificate Manager and AppViewX: https://www.appviewx.com/blogs/certificate-lifecycle-management-automation-with-aws-certificate-managerand-appviewx-avx-one-clm-2/
- G2, AWS Certificate Manager review 12246811: https://www.g2.com/products/aws-certificate-manager/reviews?expanded=aws-certificate-manager-review-12246811
- DEV Community, AWS re: Invent 2025 session recap on exportable certificates: https://dev.to/kazuya_dev/aws-reinvent-2025-automating-certificate-management-with-exportable-public-certificates-sec322-2lib
- App Developer Magazine, AWS Certificate Manager exportable certificates: https://appdevelopermagazine.com/aws-certificate-manager/
- AppViewX, Certificate lifecycle management requirements: https://www.appviewx.com/blogs/certificate-lifecycle-management-requirements/
- AppViewX, CA-agnostic vs CA-native CLM: https://www.appviewx.com/blogs/ca-agnostic-vs-ca-native-clm/
- AppViewX, What CA-agnostic really means: https://www.appviewx.com/blogs/what-ca-agnostic-really-means/
- AppViewX, Policy engine: https://www.appviewx.com/blogs/appviewx-policy-engine/
- AppViewX, It’s official: CA/B Forum votes yes to 47-day TLS certificates: https://www.appviewx.com/blogs/its-official-ca-b-forum-votes-yes-to-47-day-tls-certificates/
- Certbot, GitHub repository: https://github.com/certbot/certbot
- IETF, RFC 8555: Automatic Certificate Management Environment (ACME): https://datatracker.ietf.org/doc/html/rfc8555
Tags
About the Author