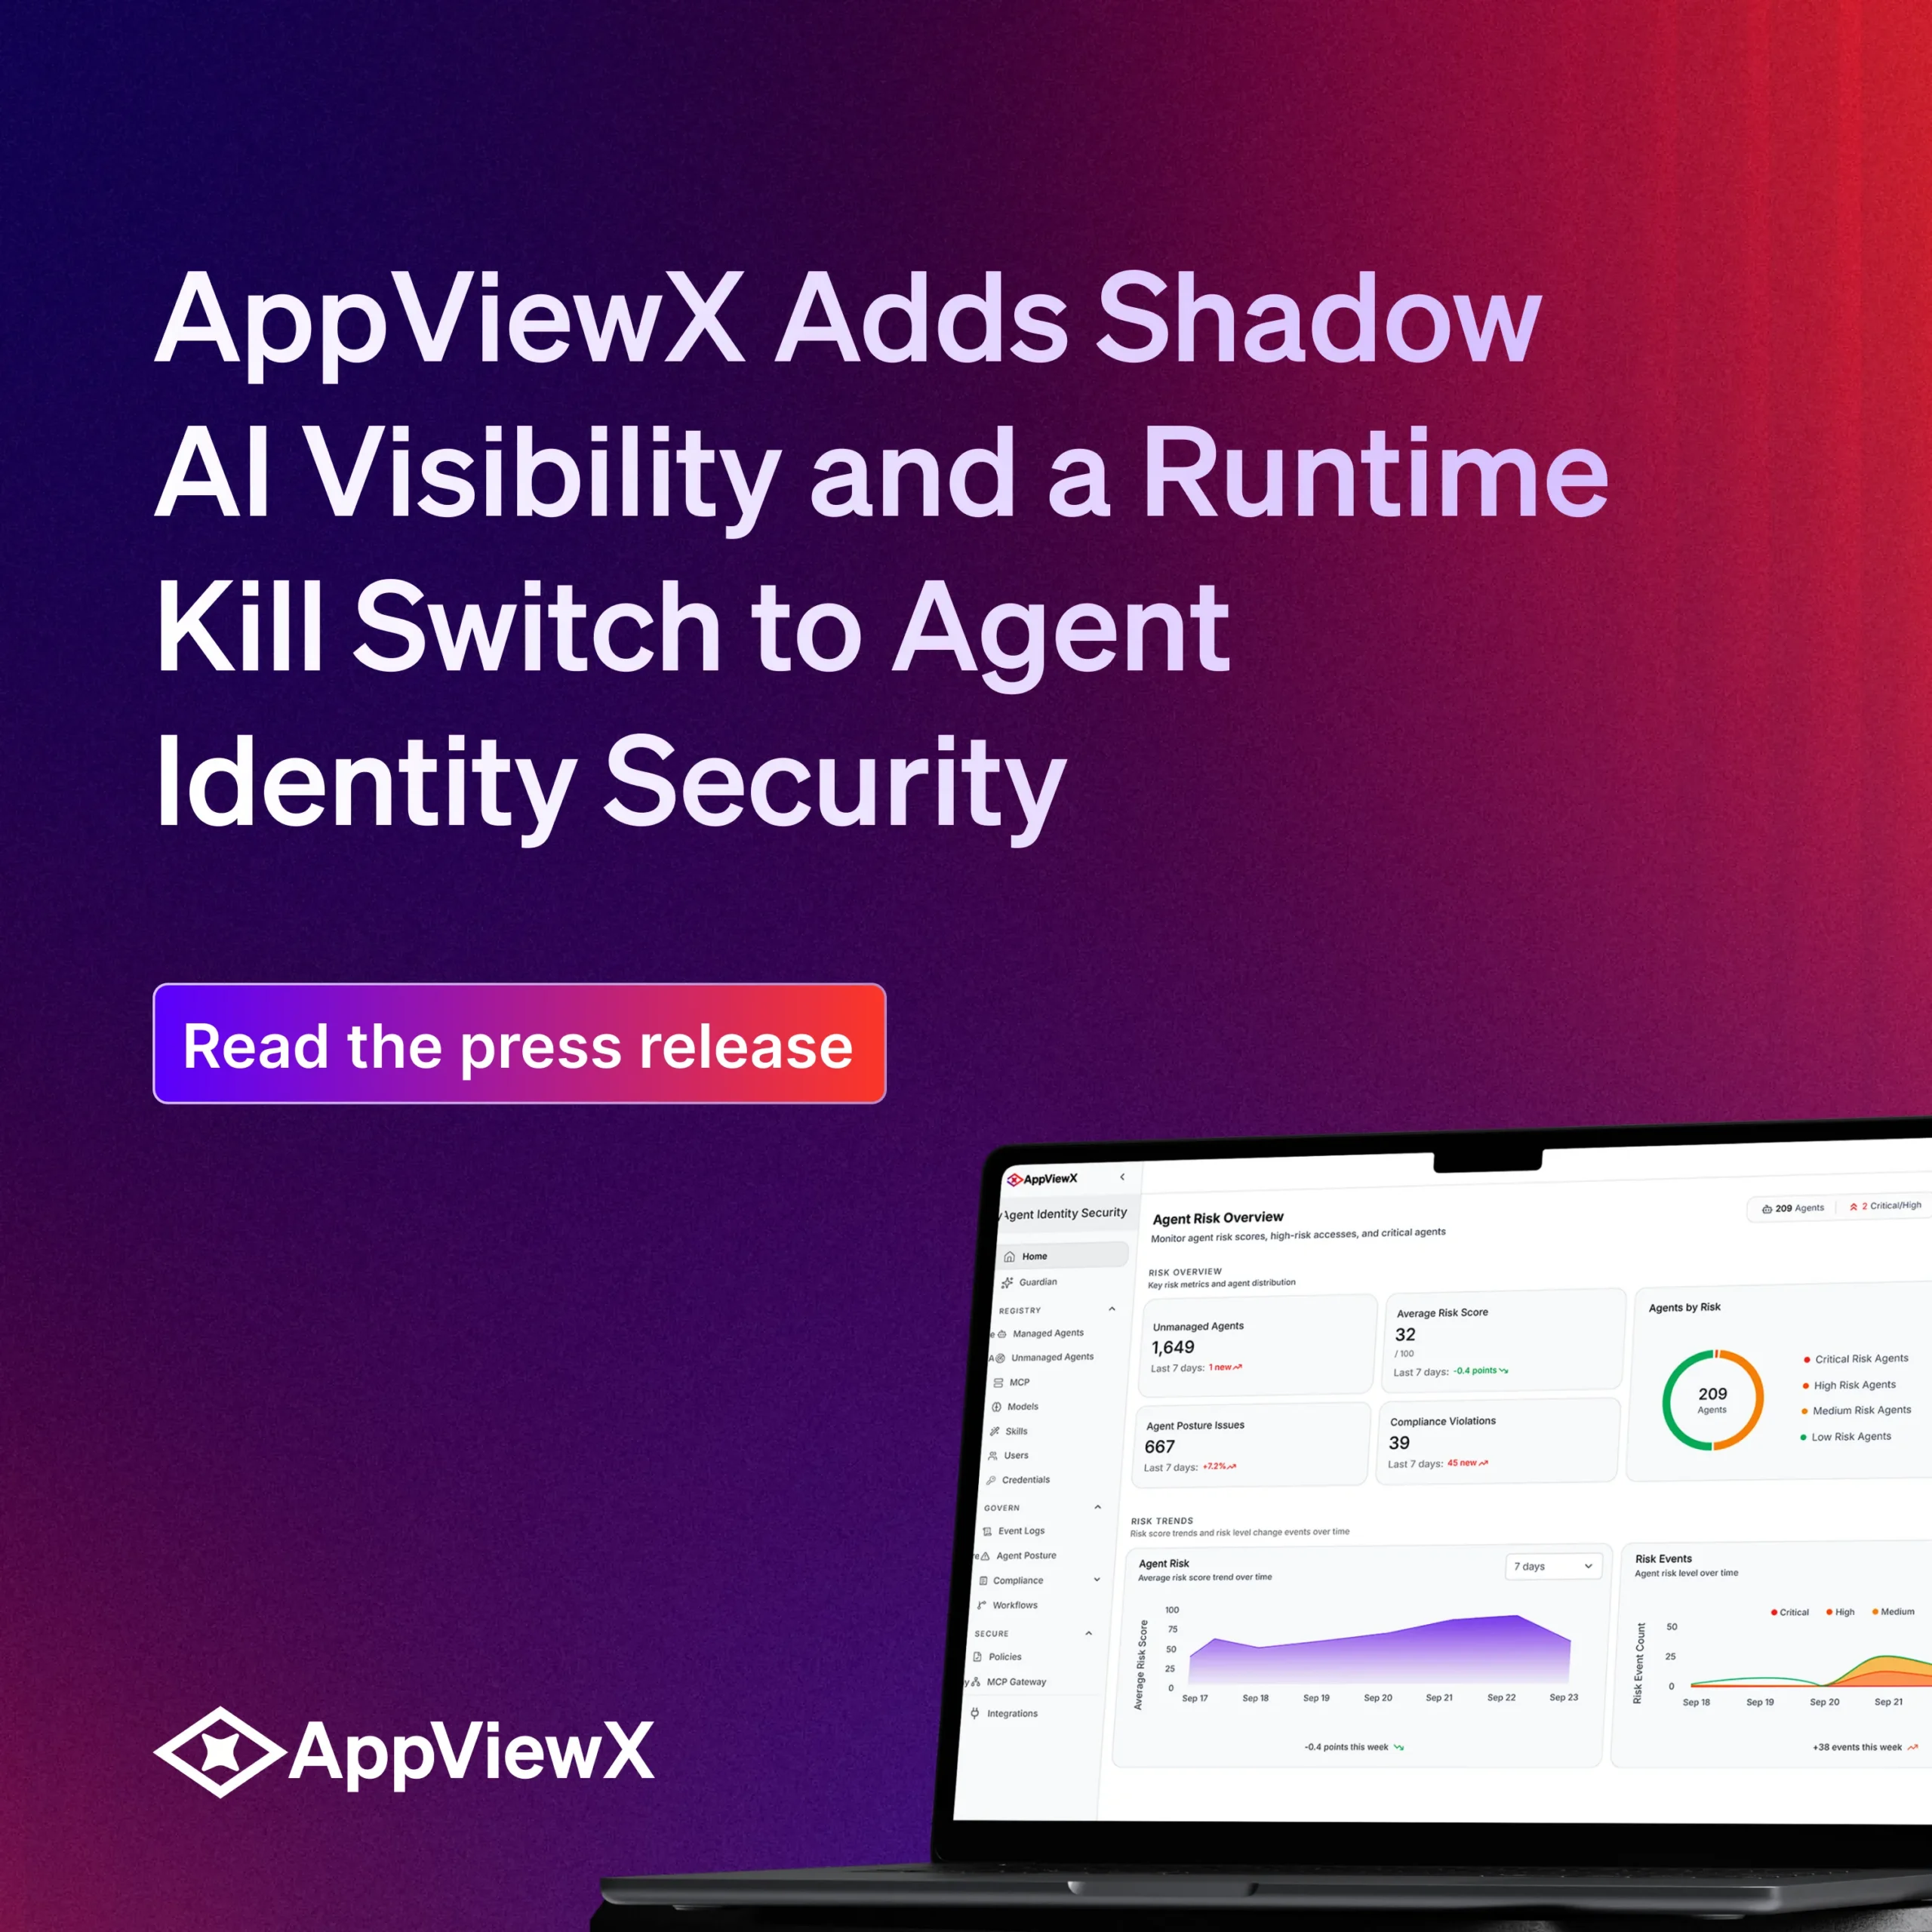
AppViewX Agent Identity Security is purpose-built for the agent identity layer. It discovers every agent, whether sanctioned or shadow; governs their posture and maintains audit-ready activity logs; and monitors and controls, in real time, every action that the agent performs.
Most comprehensive discovery, governance, and runtime security.
Discover all agent types, including coding agents, enterprise productivity agents, SaaS agents, and custom-built agents.
A comprehensive AI Bill of Materials (AIBOM) maps each agent to its users, credentials, endpoints, skills, MCP servers, and models.
Map agent posture to compliance frameworks, maintain audit-ready logs, and review activity timelines in the live access graph.
Understand token usage, trends, and costs, and set thresholds to prevent runaway spending.
Just-in-time access eliminates standing privileges, granting access to MCP servers and tools only when and for as long as needed, based on identity and context.
Block actions, revoke access, or trigger the Agent Kill Switch. It can be activated via event-driven workflows, through runtime policies, or on demand.
Agent security that fits your infrastructure, workflows, and compliance requirements.
Discover every agent through a broad range of deployment methods, including API integrations with existing EDR, SaaS, and cloud platforms, AppViewX’s endpoint Guardian agent, or the SDK.
A centralized MCP Gateway discovers sanctioned and shadow MCP servers and continuously assesses their risk and posture, applies granular least-privilege policies, and protects sensitive data exchanged between agents and MCP.
Out-of-the-box, event-driven workflows to suspend or kill agents, revoke credentials, assign owners, query agent posture issues, create Jira tickets, and send Slack messages and email notifications.
Assess and demonstrate alignment of your agent deployments against frameworks such as the OWASP Top 10 for Agentic Applications, MITRE ATLAS, GDPR, HIPAA, ISO 27001/42001, and the EU AI Act.
Built-in AI assistant that uses natural language to correlate security data across agents, users, MCP servers, and environments, surfacing high-risk agents, posture issues, and compliance insights.
Integrates with your existing security and IT ecosystem, including DLP, SIEM, ITDR, Firewall, IdP, MDM, and EDR tools, SOC workflows, and collaboration platforms like Slack and Teams.
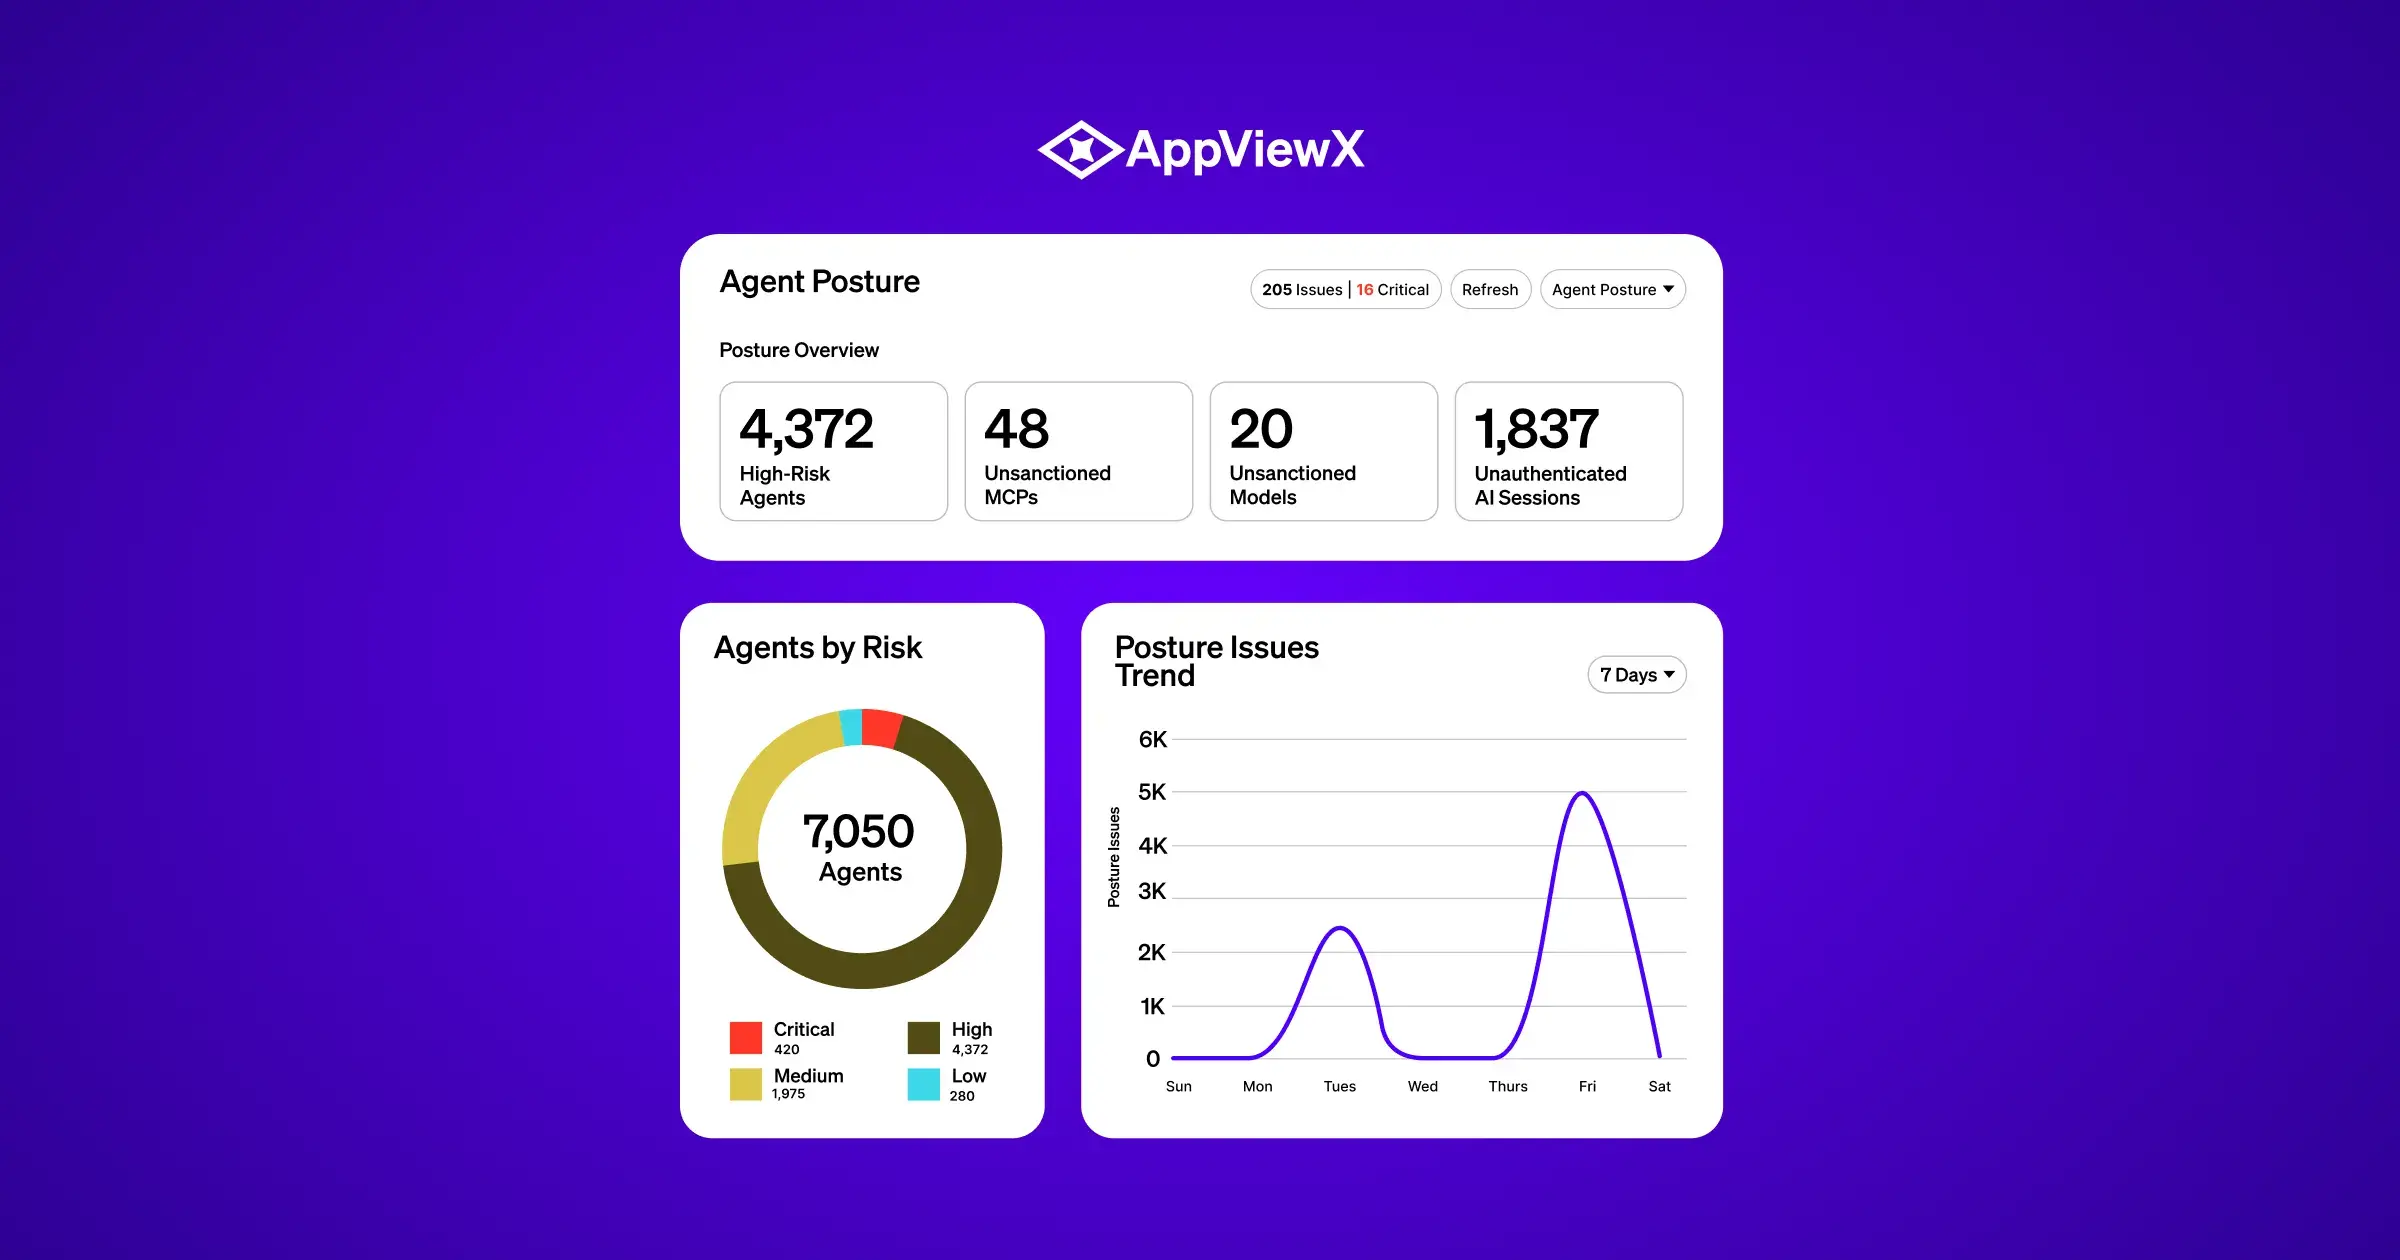
Discover agents in minutes, including shadow AI operating outside approved processes. Map your agent attack surface by connecting each agent’s identity to its users, credentials, endpoints, Skills, MCP servers, and models. Correlate access and activity to assess risk posture and prioritize high-risk agents.


Evaluate agent risk against security and compliance standards, retain auditable records throughout the agent lifecycle to investigate activity, support faster audit reviews, and demonstrate compliance. Reduce unexpected AI costs and strengthen agent security by monitoring consumption patterns and enforcing budget policies.
Terminate an agent and its active sessions automatically when triggered by events, through runtime policies, or on demand. Build event-driven workflows triggered by changes AppViewX detects, and act on third-party signals through Shared Signals Framework (SSF) integration.

Want to dive deeper and see how Agent Identity Security would impact your business?
Agent Identity Security covers every category of AI agent in the enterprise, including:
Agent Identity Security detects shadow agents by ingesting signals from:
The MCP Gateway applies real-time controls to agent-to-MCP traffic routed through it, helping identify unauthorized MCP servers and tool connections.
It also connects natively to cloud and SaaS platforms such as AWS Bedrock, Salesforce AgentForce, Copilot Studio, and more to enumerate every agent provisioned at the platform level, building a complete AIBOM for each:
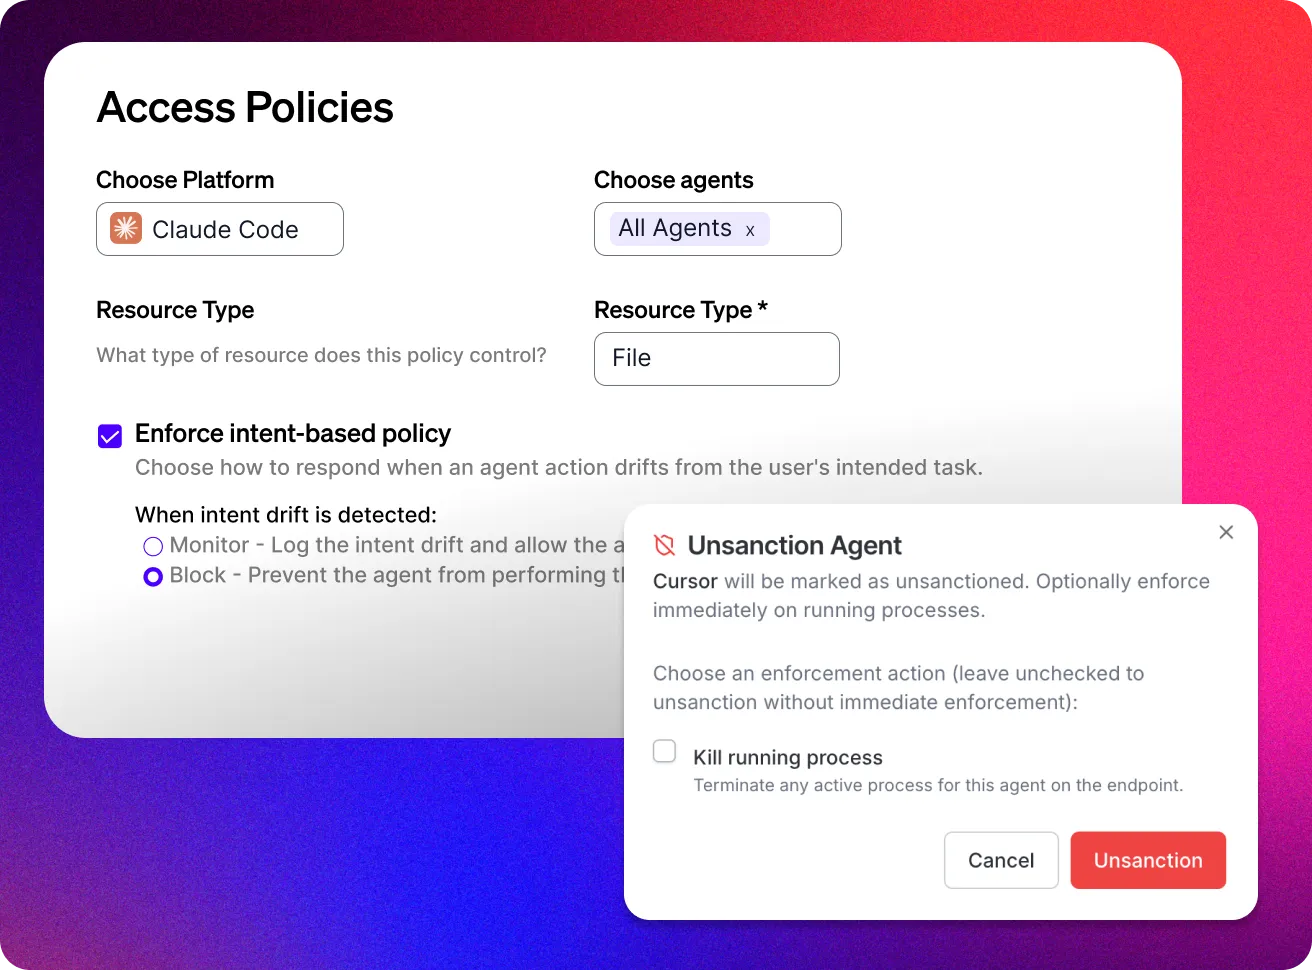
AppViewX's Agent Identity Security product enforces task-based access policies and allowlists/denylists across every action category, including:
These policies are enforced inline at runtime before any action executes, ensuring agents operate strictly within the permissions their specific task requires.
Yes. Agent Identity Security blocks policy-violating actions inline before they execute, and the Agent Kill Switch lets you terminate any agent session instantly, either:
InfinityAI, the in-product assistant formerly known as Guardian AI, is ready to investigate findings, surface prioritized remediation steps, and guide your team from detection to resolution from day one.
The Agent Identity Security product from AppViewX governs agents from creation to decommission via automated workflows. At deployment/installation, it:
Discover, automate, and secure machine and agent identities across your entire enterprise.